Getting ISO 27001 certification is a significant achievement. It shows that your organization has established a structured approach to managing information security risks.
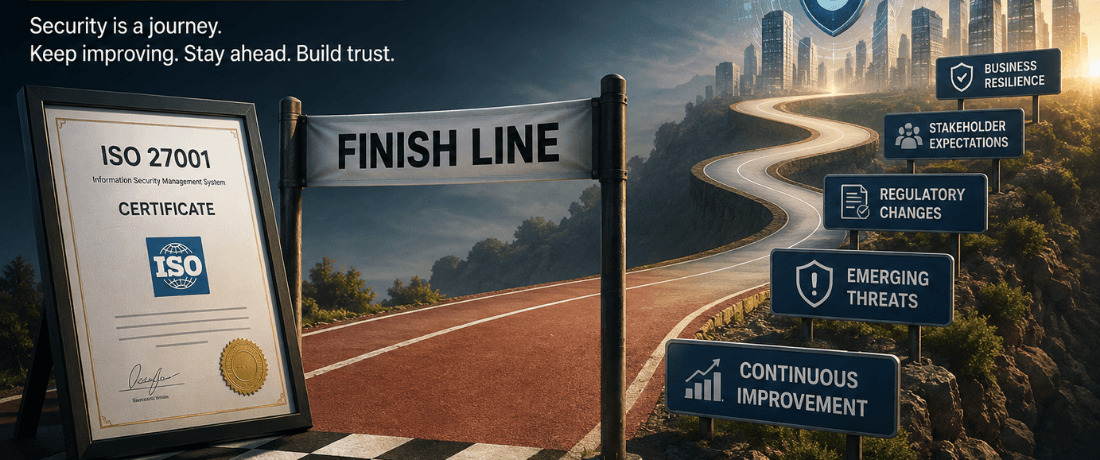
But certification is not the finish line.
It is the starting point for continuously improving your Information Security Management System (ISMS).
What Happens After ISO 27001 Certification?
Your business doesn’t stay the same after certification.
New employees join, systems change, cloud environments expand, new vendors are onboarded, and cyber threats continue to evolve. Your security processes need to evolve with them.
That’s why organizations should continuously do the following:
- Review and update information-security risks
- Conduct regular internal audits
- Monitor the effectiveness of security controls
- Assess third-party and vendor risks
- Train employees on security awareness
- Test incident-response procedures
- Review and improve the ISMS
An ISO 27001 certificate demonstrates that your management system met the applicable requirements at the time of assessment. Maintaining an effective ISMS requires ongoing monitoring, review, and improvement.
Why Continuous Improvement Matters
A common mistake is treating ISO 27001 as a compliance project that ends once the certificate is obtained.
A better approach is:
Assess → Improve → Monitor → Measure → Review → Repeat
This helps organizations stay prepared for changing risks while getting more business value from their ISO 27001 investment.
Internal audits, risk assessments, and management reviews should therefore be viewed as tools for improving security, not simply as preparation for the next certification audit.
Your Certificate Is Only Part of the Journey
ISO 27001 can provide a strong foundation for managing information security, but its real value comes from how effectively your organization uses the framework every day.
The goal shouldn’t simply be:
“How do we maintain our ISO 27001 certificate?”
Instead, ask:
“How can we make our information-security management system stronger every year?”
That’s the mindset that turns ISO 27001 from a certification into a long-term business capability.
Take the Next Step with CUNIX
Already ISO 27001 certified but unsure whether your ISMS is still effective?
CUNIX can help you identify gaps, strengthen your information-security processes, prepare for audits, and build a culture of continuous improvement.
👉 Explore CUNIX’s ISO 27001 Certification Services
Don’t just maintain your certificate. Make your ISO 27001 framework work harder for your business.